Detection-as-Code — every authored rule is version-controlled,
ATT&CK-mapped, tested against real adversary telemetry, and scored for
precision, recall and false-positive rate against labelled events. Rules
that miss the bar they declare fail the build.
View source on GitHub →
20authored detections
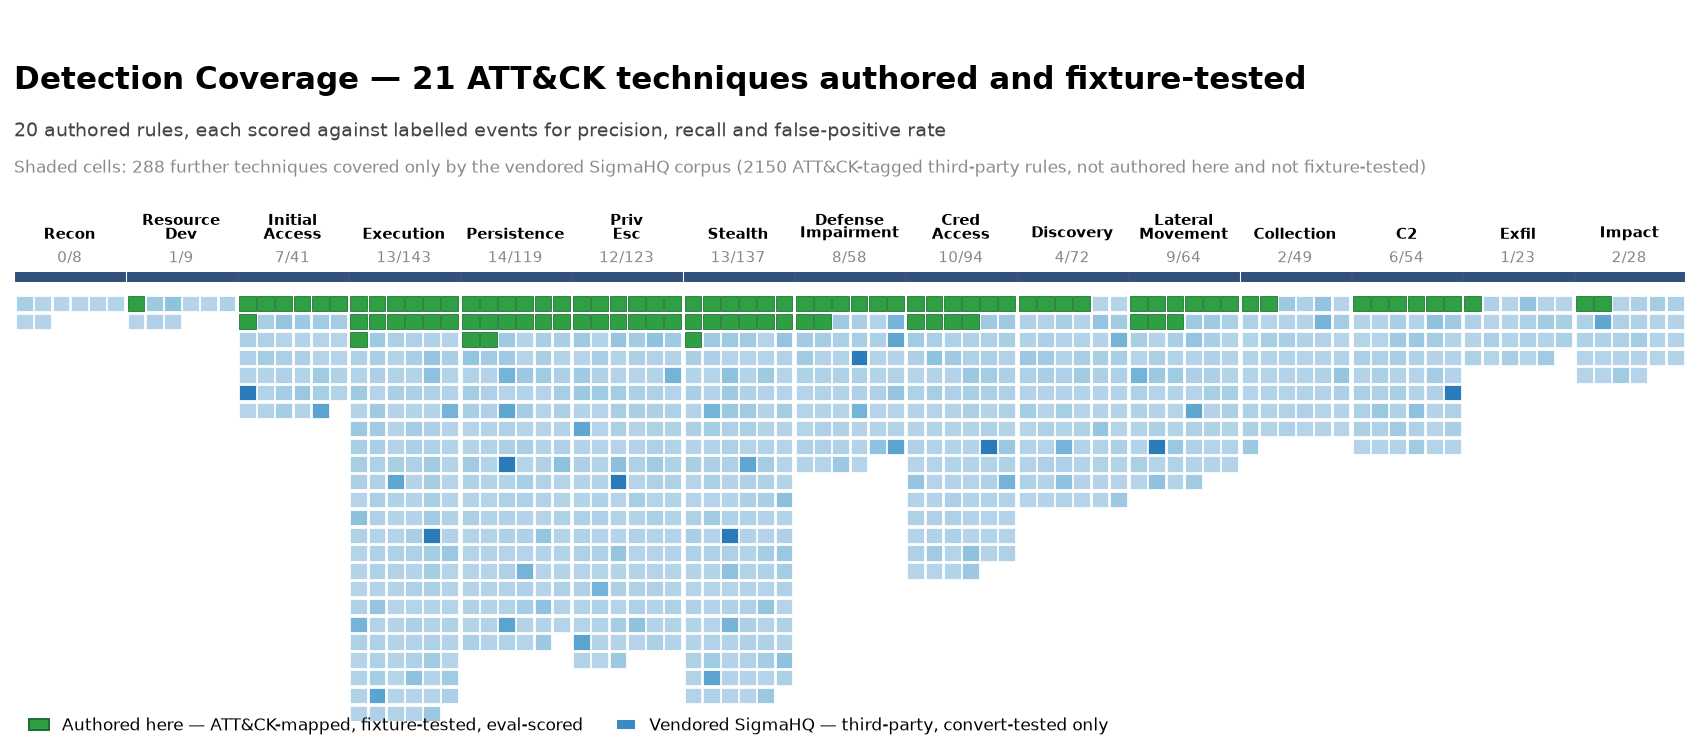
21ATT&CK techniques authored
20scored for precision/recall
172labelled eval events
16fixture-tested on real EVTX
18pinned EVTX samples
Hover any number — every metric on this page explains how it
is calculated and where its data comes from. For the full picture, read
How it works.
Separately, a pinned copy of the public SigmaHQ Windows corpus
(2,399 third-party rules, 100% convert rate) is run
through the same conversion pipeline and adds 288 further
techniques to the map below. That corpus is not authored here and is not
held to the fixture or eval gates.
Authored detections
My own rules. Read FP rate first: precision moves with
the malicious-to-benign ratio in each case set, which is authored rather than
observed, while FP rate and recall do not. The 2,399 vendored SigmaHQ
rules are not listed here; they only feed the coverage map above.